An assistant can read your code. It cannot watch your site.
Ask an AI to audit your app and it reads the repository. Regulators, plaintiffs' scanners and careful customers never see the repository. They load the live site, and the live site is the build plus everything added since: the tag a marketer put in Tag Manager, the chat widget, the CMS embed, the redesign that dropped the privacy link. Webopsy loads it in a real browser and records what actually happens. The report and every fix are free. What we charge for is doing it again after every deploy, and keeping the record.
Evidence, not a checklist.
Each tracker finding says what the browser saw and when, for example: Meta Pixel sent data 0.8 seconds after load, to facebook.com, before anyone answered a banner. Session recorders are called out separately, because recording visitors before consent is what US wiretap claims are built on. None of it is visible in your code if the tag arrives through a tag manager.
Your policy, against your site.
A privacy policy can be complete on paper and still not describe the site. The scan compares what your policy says with what the browser saw: ad pixels while the policy never mentions advertising, a session recorder while it never mentions recording. Then it writes the policy that matches, and the banner that holds those tags until a visitor agrees.
Watched after every deploy.
Watch re-checks the site every day and within a minute of every deploy, through a deploy hook or a GitHub Action that fails the job when something regressed (the Action alone is free). You get an email, a dated record of every check, and a trust page that answers the questions vendor reviews ask, from live evidence. The Clean Bill of Health stays in force while the site deserves it.
The report and every fix: free. Watch: $19 a month per site. Or a person implements every fix for $499, or audits the backend for $1,500. Pricing
What each score covers.
- Privacy
- Privacy policy present and complete (the fourteen disclosures GDPR, CCPA and PIPEDA expect), cookie consent before trackers fire, cookie policy, Do-Not-Sell link, children's data, newsletter consent.
- Security
- HTTPS and mixed content, the security headers, secret keys shipped in the bundle, Supabase and Firebase left open, a security.txt so researchers can reach you.
- Legal
- Terms of service, a way to contact you, and the legal identity and address that Stripe, the app stores and EU law expect to see.
- Accessibility and design
- WCAG 2.2 A/AA violations from axe-core, run on the live page in a real browser. And the detector for the patterns visitors read as AI-generated, each one marked on a screenshot of your page.
When something cannot be verified from outside, the report says so instead of guessing. What is and is not checked.
What the report contains.
A document you can hand to a developer, a co-founder or counsel. Pages below are from the example.com report above; with Watch it also comes as a PDF.
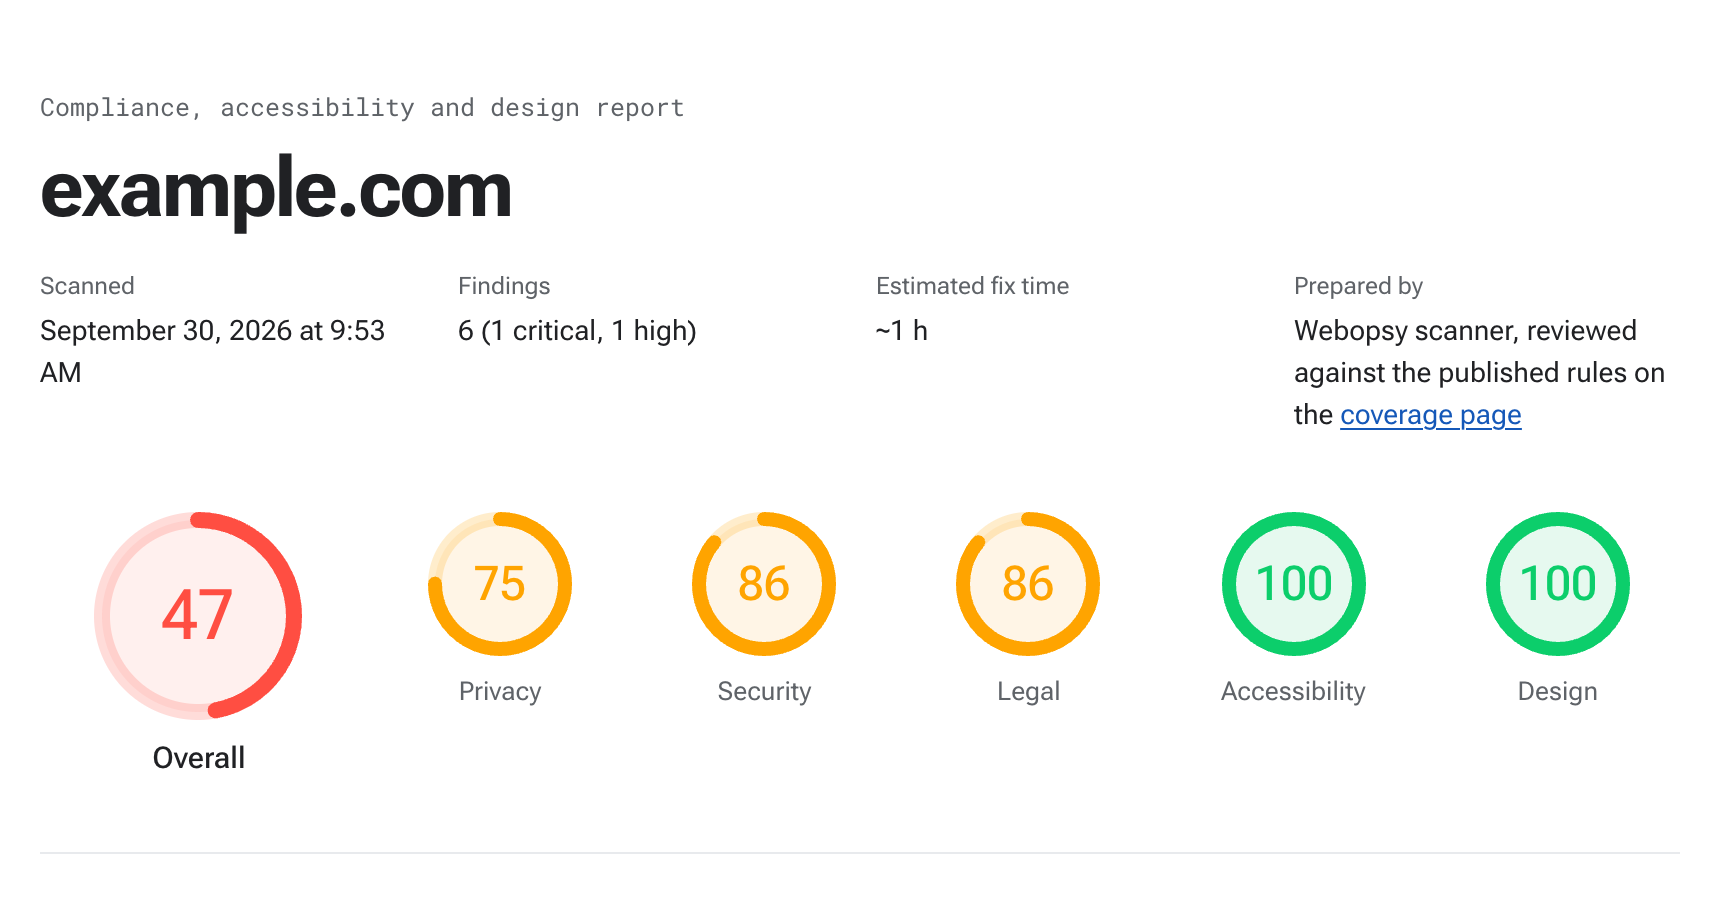 Cover. Six scores, findings count, total fix time.
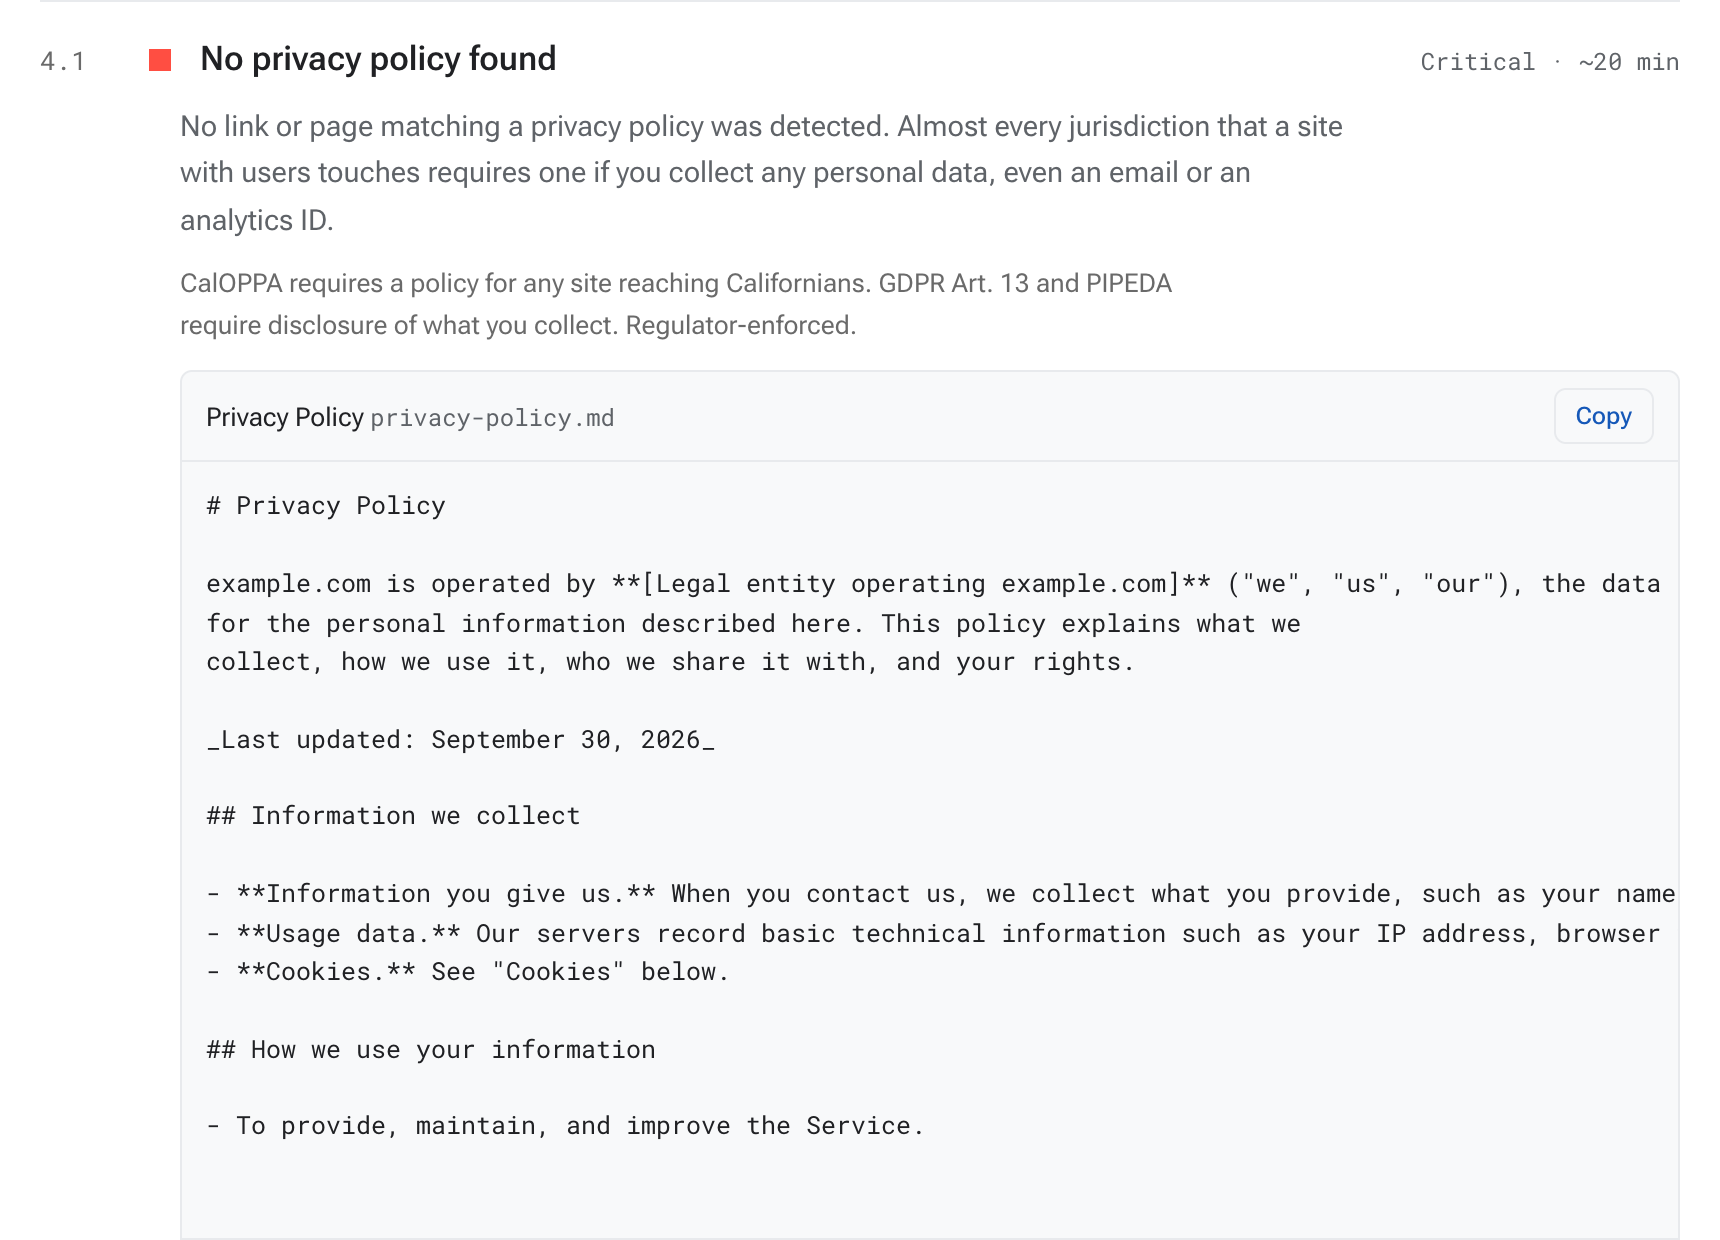 Every finding with the law it maps to and the fix, inline.
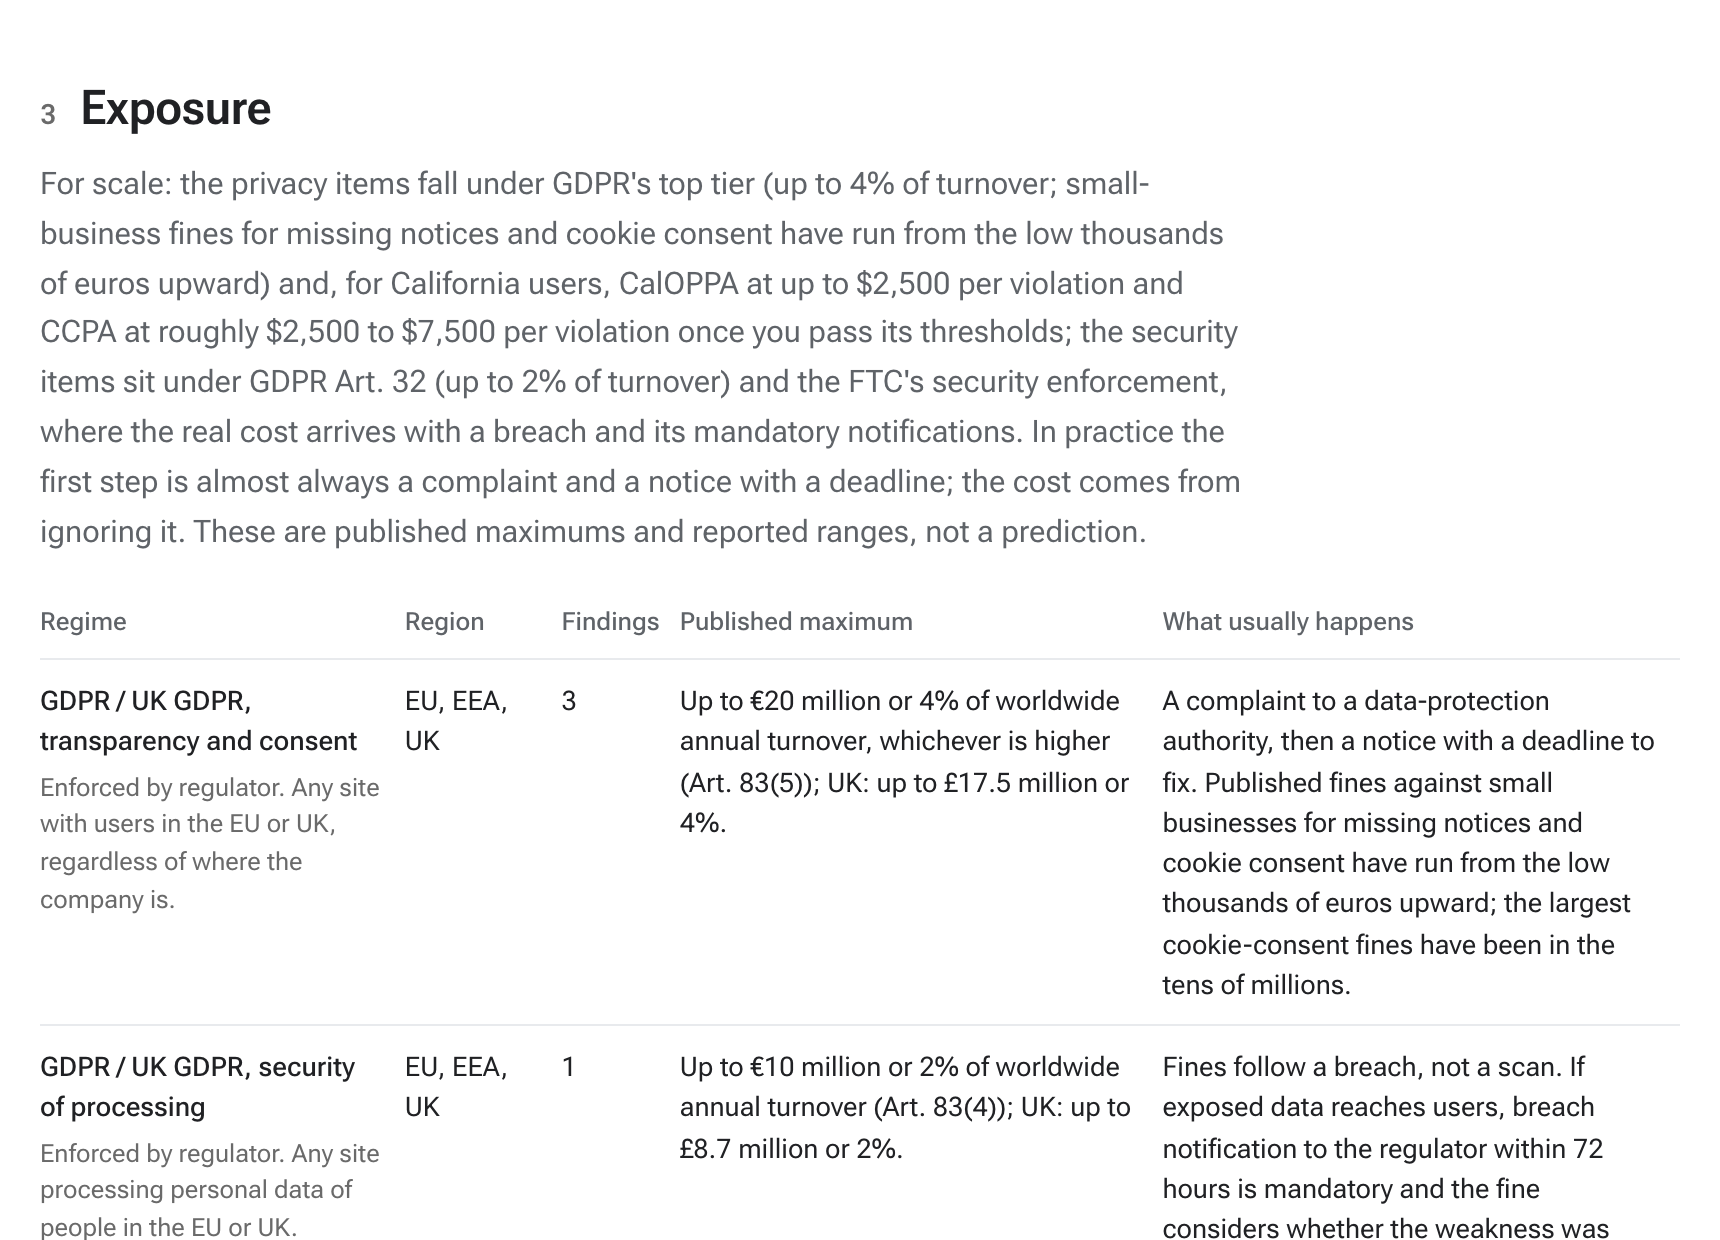 Statutory exposure per regime. Published maximums, and what usually happens in practice.
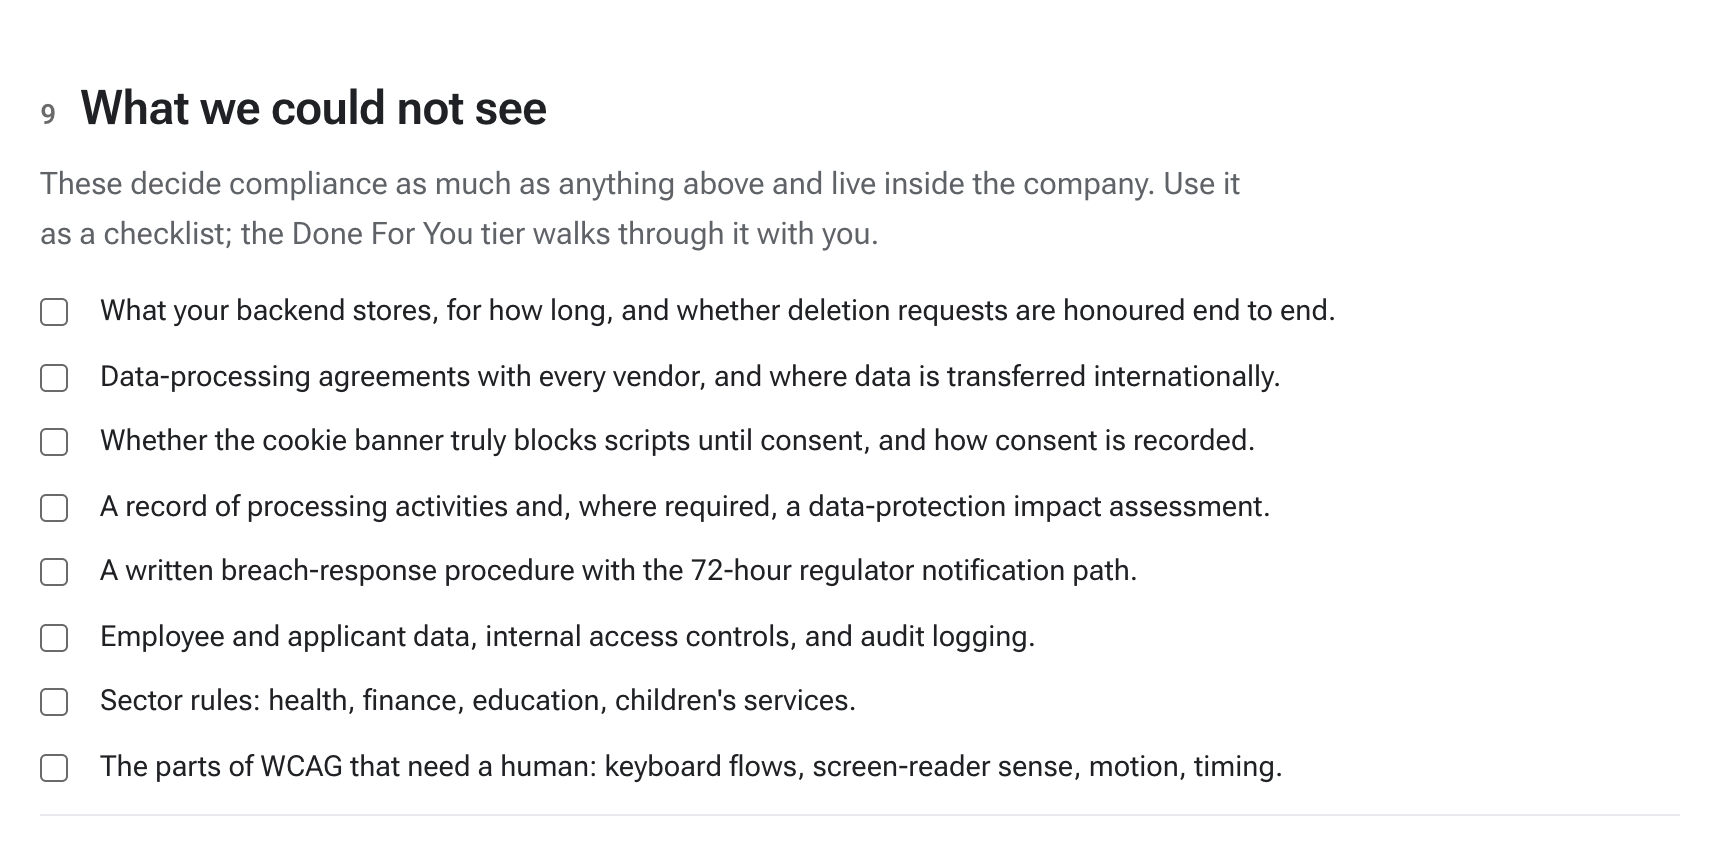 What no outside scan can see, so nobody mistakes a clean score for a guarantee.