This report was prepared for grablo.co. It shows the top findings; the full report includes every issue and its fix.
What the scores mean
No change since the scan on Nov 15, 2026.
Clean bill of health since Oct 16, 2026, serial WO-2026-2140. View the certificate
Opportunities
These are the issues most likely to matter to a regulator, an app store, or an attacker. Fix them first.
Elements must meet minimum color contrast ratio thresholds (29 elements)~3 h
Ensure the contrast between foreground and background colors meets WCAG 2 AA minimum contrast ratio thresholds Example: <div class="mk-eyebrow">Grablo Reflex</div>
WCAG wcag2aa, wcag143. Web accessibility is enforced under the ADA (US, thousands of private suits a year), Section 508, the European Accessibility Act, the UK Equality Act, and AODA (Ontario).
Diagnostics
Worth fixing. Not an emergency.
Missing 3 security headers~15 min
Not set: Content-Security-Policy, X-Content-Type-Options, X-Frame-Options. These defend against clickjacking, MIME sniffing, and protocol downgrade.
// next.config.js — Missing on your site: Content-Security-Policy, X-Content-Type-Options, X-Frame-Options. The Content-Security-Policy below already allows Google Fonts; add the domain of anything else you load to script-src or connect-src, then re-scan.
/** @type {import('next').NextConfig} */
const securityHeaders = [
  { key: 'Strict-Transport-Security', value: "max-age=63072000; includeSubDomains; preload" },
  { key: 'X-Content-Type-Options', value: "nosniff" },
  { key: 'X-Frame-Options', value: "SAMEORIGIN" },
  { key: 'Referrer-Policy', value: "strict-origin-when-cross-origin" },
  { key: 'Permissions-Policy', value: "camera=(), microphone=(), geolocation=()" },
  { key: 'Content-Security-Policy', value: "default-src 'self'; script-src 'self' 'unsafe-inline'; connect-src 'self'; img-src 'self' data: https:; style-src 'self' 'unsafe-inline' https://fonts.googleapis.com; font-src 'self' data: https://fonts.gstatic.com; frame-src 'none'; frame-ancestors 'self'; base-uri 'self'; form-action 'self'" },
];

module.exports = {
  async headers() {
    return [{ source: '/:path*', headers: securityHeaders }];
  },
};Zooming and scaling must not be disabled~10 min
Ensure <meta name="viewport"> does not disable text scaling and zooming Example: <meta name="viewport" content="width=device-width, initial-scale=1.0, maximum-scale=1.0, user-scalable=no, interactive-widget=resizes-visual">
WCAG wcag2aa, wcag144. Web accessibility is enforced under the ADA (US, thousands of private suits a year), Section 508, the European Accessibility Act, the UK Equality Act, and AODA (Ontario).
No security.txt for vulnerability reports~5 min
A /.well-known/security.txt file tells researchers how to report a problem before it becomes a breach. Two lines: Contact and Expires.
RFC 9116; expected by many bug-bounty and disclosure norms.
What these findings expose you to
For scale: the security items sit under GDPR Art. 32 (up to 2% of turnover) and the FTC's security enforcement, where the real cost arrives with a breach and its mandatory notifications; the accessibility violations are the kind that draw private ADA suits, thousands a year, usually settled for $5,000 to $25,000 plus the plaintiff's fees. In practice the first step is almost always a complaint and a notice with a deadline; the cost comes from ignoring it. These are published maximums and reported ranges, not a prediction.
GDPR / UK GDPR, security of processing · EU, EEA, UK1 finding
Maximum. Up to €10 million or 2% of worldwide annual turnover (Art. 83(4)); UK: up to £8.7 million or 2%.
Usually. Fines follow a breach, not a scan. If exposed data reaches users, breach notification to the regulator within 72 hours is mandatory and the fine considers whether the weakness was known.
Applies: Any site processing personal data of people in the EU or UK. Enforced by regulators.
ADA Title III and California's Unruh Act (web accessibility) · United States2 findings
Maximum. The ADA carries no fixed fine for private suits, but the defendant typically pays the plaintiff's attorney fees; California's Unruh Act adds statutory damages of $4,000 per violation. DOJ actions can carry civil penalties up to $75,000 for a first violation.
Usually. Thousands of private lawsuits a year, most against small and mid-sized sites, usually settled for roughly $5,000 to $25,000 plus fees. Fixing the automated violations is the cheapest defence.
Applies: Any business website in the US; California residents can sue under Unruh. Enforced by regulators and private plaintiffs.
European Accessibility Act / UK Equality Act / AODA · EU, UK, Ontario2 findings
Maximum. Set by each EU member state since June 2025; AODA penalties up to CA$100,000 per day for corporations; UK Equality Act claims are private.
Usually. Complaints and compliance orders first; fines are reserved for refusal to fix.
Applies: Consumer-facing digital services in the EU; Ontario organisations; UK service providers. Enforced by regulators and private plaintiffs.
FTC Act §5 (unfair or deceptive practices) and state breach laws · United States1 finding
Maximum. No fixed fine for a first violation; the FTC obtains consent orders with 20-year audit obligations, and violating an order costs over $53,000 per day. State breach-notification laws add per-resident notification costs and, in some states, per-record penalties.
Usually. Enforcement follows an incident. An exposed live key or open database is the incident waiting to happen; the practical cost is fraud on the account plus mandatory notification.
Applies: Any US company holding consumer data. Enforced by regulators.
AI design tells
16 patterns on this page read as AI-generated: AI color palette, Kicker / eyebrow label above heading, Tiny numbered section labels. Visitors have learned to recognize these; they read as a template and cost trust. Each one has a specific fix.
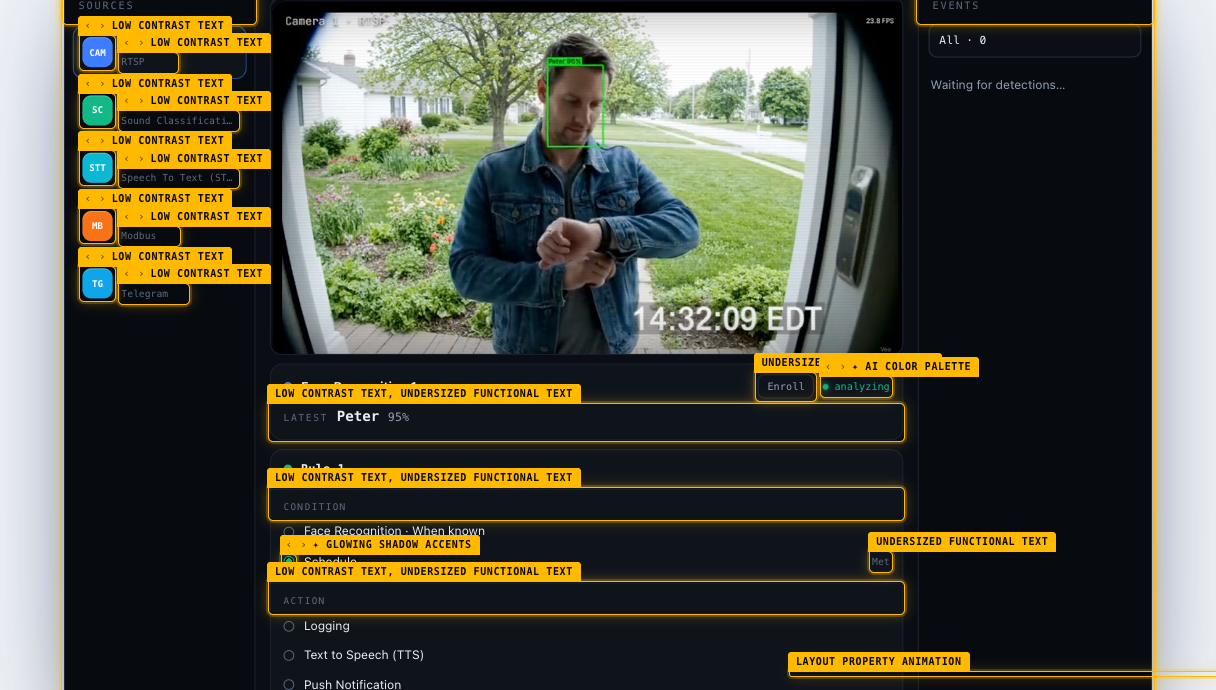
AI color palette3×
Purple/violet gradients and cyan-on-dark are the most recognizable tells of AI-generated UIs. Choose a distinctive, intentional palette.
Example: Cyan neon text on dark background
Kicker / eyebrow label above heading3×
A tiny tracked uppercase or small-caps label sitting as its own block directly above a heading is banned outright, repeated or not. Generated kickers never earn their place: the heading carries its own weight. Delete the label and let the heading speak; if the words matter, work them into the heading or the body.
Example: kicker "How it works" above h2 "A rule is a single sentence"
Tiny numbered section labels3×
Small numeric index labels riding next to section headings, repeated section after section, are AI editorial scaffolding — a page numbering its own chapters instead of earning structure. Let hierarchy, content, and rhythm carry the sequence.
Example: tiny numbered label "01" beside h3 "Create a rule" (3 on page)
Glowing shadow accents2×
Colored glow shadows — a zero-offset chromatic halo (box- or text-shadow) on any background, or any colored blurred shadow on a dark background — are the default "cool" look of AI-generated UIs. Use neutral elevation shadows and subtle, purposeful lighting instead.
Example: Zero-offset box-shadow glow (#3d7bff)
Hero eyebrow / pill chip1×
A tiny uppercase letter-spaced label sitting immediately above an oversized hero headline — or the same shape rendered as a pill chip — is now the default AI SaaS hero. Drop the eyebrow, integrate the kicker into the headline, or run it as a navigation breadcrumb instead.
Example: eyebrow chip (tracked-caps) "Grablo Reflex" above h1 "Beyond alerts. Reflex takes action."
Hairline border with wide shadow1×
A hairline border paired with a wide, diffuse shadow is a recurring generated-UI signature. Commit to one — a defined edge or a soft elevation — rather than both at once.
Example: 1px border + 140px shadow blur
Pulsing status dot1×
Small pulsing status dots simulate liveness decoratively. Reserve pulse animation for indicators tied to genuinely live, changing data; a static indicator with clear labeling is honest and calmer.
Example: .rxd-live::before — 6x6px dot with infinite "rxd-blink" animation
Radial-gradient background halo1×
A chromatic radial-gradient wash — saturated at the center, fading to transparent — used as a decorative background glow on a dark page. Same tell as glowing shadows, drawn with a gradient instead of a shadow. Ground the surface with a solid or subtly shifted background instead.
Example: radial-gradient halo (#12b886 → transparent) on dark page
Repeating-gradient stripes1×
Repeating-gradient stripes used as surface decoration are a recurring generated-UI signature. Reach for a deliberate texture or leave the surface plain.
Example: repeating-gradient decorative stripes
Undersized functional text · quality33×
Interactive and content-bearing UI text (links, buttons, nav items, labels, table cells, meta rows, timecodes) below 11px is a legibility failure, not a style choice. WCAG sets no absolute pixel floor, but functional text under 11px is a defensible quality bar: it fails on high-DPI and small viewports and it degrades tap and read targets. The 11px floor holds even inside a footer; only non-interactive legal smallprint gets the softer 10px floor. Being ON the DESIGN.md size ramp does not exempt a value here: adding 8px to the ramp launders the token but not the legibility problem, and that is exactly the escape hatch this rule closes. Exempts sup/sub, visually-hidden (sr-only) text, and code/terminal contexts. Decorative letterspaced micro-labels are still functional and stay in scope.
Example: 10.5px functional text "v1.27" (below 11px floor)
Low contrast text · quality27×
Text does not meet WCAG AA contrast requirements (4.5:1 for body, 3:1 for large text). Increase the contrast between text and background.
Example: 4.50:1 (need 4.5:1) — text #087f5b on #f1f3f5
Tight line height · quality7×
Line height below 1.3x the font size makes multi-line text hard to read. Use 1.5 to 1.7 for body text so lines have room to breathe.
Example: line-height 1.15x (need >=1.3)
Layout property animation · quality2×
Animating width, height, padding, or margin causes layout thrash and janky performance. Use transform and opacity instead, or grid-template-rows for height animations.
Example: transition: margin
Wide letter spacing on body text · quality1×
Letter spacing above 0.05em on body text disrupts natural character groupings and slows reading. Reserve wide tracking for short uppercase labels only.
Example: letter-spacing: 0.10em on body text
Full annotated page (86 labels)

This report is complete and free, and true as of the scan time above. The next deploy, a tag added in Tag Manager or a redesigned footer can change it. Watch re-checks grablo.co every day and after every deploy, emails you the moment something regresses, keeps the dated record, and gives you a trust page your customers can check.
Watch grablo.coTrust page draftPassed audits
(11)
Privacy policy is present
A privacy policy link or page was found.
Privacy policy covers the expected disclosures
2286 words; 14 disclosure checks passed; last updated May 7, 2026.
No third-party trackers detected
None of the common analytics or marketing pixels were found in the page.
Terms of service are present
A terms page or link was found.
Public contact or business identity present
A contact email, contact page, or mailto link was found.
No secret keys in the page or its scripts
No server-side keys (Stripe secret, OpenAI, Anthropic, AWS, GitHub, Slack, SendGrid, Supabase service_role, private keys) in the page or the 6 script bundles it loads.
1 security header set
Strict-Transport-Security
No mixed content
All referenced resources use HTTPS.
Legal entity and address are shown
A company name and a postal address appear on the page.
Served over HTTPS
The final URL uses TLS.
22 accessibility rules passed
Rules axe-core tested and found no violations for.
Share this report.
The link is public and shows the same free view you see here; nothing about the reader is recorded.
The certificate.
grablo.co holds Clean Bill of Health WO-2026-2140, last checked November 22, 2026. Open it for the seal and what it verified.
Put your score on your README.
An embeddable badge that re-checks weekly. Builders use it the way they use a CI badge: proof the boring stuff is handled.
[](https://webopsy.tech/s/grablo.co)