This report was prepared for thisiscoco.app. It shows the top findings; the full report includes every issue and its fix.
What the scores mean
Clean bill of health since Nov 22, 2026, serial WO-2026-5223. View the certificate
Opportunities
No critical or high-severity issues. That's the bar most sites miss.
Diagnostics
Worth fixing. Not an emergency.
Privacy policy is missing 3 expected disclosures~45 min
Not found in the policy text: addresses children's data; mentions the right to complain to a regulator; carries a last-updated or effective date. Last updated 7 November 2026.
COPPA; GDPR Art. 8 · GDPR Art. 13(2)(d) · CCPA §1798.130(a)(5) (annual update); good practice everywhere
<!-- Sections your privacy policy at https://thisiscoco.app/privacy does not have.
     Paste each under a heading of its own, in the order shown, and update the
     date at the top of the policy. -->

_Last updated: November 22, 2026_

## Complaints

If you are unhappy with how we handle your information, tell us first at [[email protected]]. You may also lodge a complaint with your data-protection authority (in the UK, the ICO; in the EEA, the supervisory authority of your country).

## Children

The Service is not directed to children under 13 (or the minimum age in your
country), and we do not knowingly collect their data. If you believe a child has
provided us information, contact us and we will delete it.

---
_Generated from what the scanner observed on thisiscoco.app on November 22, 2026. Confirm each section matches what you actually do; not legal advice._Missing 3 security headers~15 min
Not set: Content-Security-Policy, X-Content-Type-Options, X-Frame-Options. These defend against clickjacking, MIME sniffing, and protocol downgrade.
# Missing on your site: Content-Security-Policy, X-Content-Type-Options, X-Frame-Options. The Content-Security-Policy below already allows only your own origin; add the domain of anything else you load to script-src or connect-src, then re-scan.
Strict-Transport-Security: max-age=63072000; includeSubDomains; preload
X-Content-Type-Options: nosniff
X-Frame-Options: SAMEORIGIN
Referrer-Policy: strict-origin-when-cross-origin
Permissions-Policy: camera=(), microphone=(), geolocation=()
Content-Security-Policy: default-src 'self'; script-src 'self'; connect-src 'self'; img-src 'self' data: https:; style-src 'self' 'unsafe-inline'; font-src 'self' data:; frame-src 'none'; frame-ancestors 'self'; base-uri 'self'; form-action 'self'

# Vercel (vercel.json):
{
  "headers": [
    {
      "source": "/(.*)",
      "headers": [
        {
          "key": "Strict-Transport-Security",
          "value": "max-age=63072000; includeSubDomains; preload"
        },
        {
          "key": "X-Content-Type-Options",
          "value": "nosniff"
        },
        {
          "key": "X-Frame-Options",
          "value": "SAMEORIGIN"
        },
        {
          "key": "Referrer-Policy",
          "value": "strict-origin-when-cross-origin"
        },
        {
          "key": "Permissions-Policy",
          "value": "camera=(), microphone=(), geolocation=()"
        },
        {
          "key": "Content-Security-Policy",
          "value": "default-src 'self'; script-src 'self'; connect-src 'self'; img-src 'self' data: https:; style-src 'self' 'unsafe-inline'; font-src 'self' data:; frame-src 'none'; frame-ancestors 'self'; base-uri 'self'; form-action 'self'"
        }
      ]
    }
  ]
}

# Netlify / Cloudflare Pages (_headers):
/*
  Strict-Transport-Security: max-age=63072000; includeSubDomains; preload
  X-Content-Type-Options: nosniff
  X-Frame-Options: SAMEORIGIN
  Referrer-Policy: strict-origin-when-cross-origin
  Permissions-Policy: camera=(), microphone=(), geolocation=()
  Content-Security-Policy: default-src 'self'; script-src 'self'; connect-src 'self'; img-src 'self' data: https:; style-src 'self' 'unsafe-inline'; font-src 'self' data:; frame-src 'none'; frame-ancestors 'self'; base-uri 'self'; form-action 'self'

# nginx:
add_header Strict-Transport-Security "max-age=63072000; includeSubDomains; preload" always;
add_header X-Content-Type-Options "nosniff" always;
add_header X-Frame-Options "SAMEORIGIN" always;
add_header Referrer-Policy "strict-origin-when-cross-origin" always;
add_header Permissions-Policy "camera=(), microphone=(), geolocation=()" always;
add_header Content-Security-Policy "default-src 'self'; script-src 'self'; connect-src 'self'; img-src 'self' data: https:; style-src 'self' 'unsafe-inline'; font-src 'self' data:; frame-src 'none'; frame-ancestors 'self'; base-uri 'self'; form-action 'self'" always;No legal entity name or address~5 min
Sites that take money or serve EU/German users are expected to show who runs them and where. It also unblocks Stripe and app-store reviews.
GDPR Art. 13(1)(a) (controller identity); German TMG §5 Impressum; EU e-Commerce Directive Art. 5; consumer-protection rules in most countries.
No security.txt for vulnerability reports~5 min
A /.well-known/security.txt file tells researchers how to report a problem before it becomes a breach. Two lines: Contact and Expires.
RFC 9116; expected by many bug-bounty and disclosure norms.
What these findings expose you to
For scale: the privacy items fall under GDPR's top tier (up to 4% of turnover; small-business fines for missing notices and cookie consent have run from the low thousands of euros upward) and, for California users, CalOPPA at up to $2,500 per violation and CCPA at roughly $2,500 to $7,500 per violation once you pass its thresholds; the security items sit under GDPR Art. 32 (up to 2% of turnover) and the FTC's security enforcement, where the real cost arrives with a breach and its mandatory notifications. In practice the first step is almost always a complaint and a notice with a deadline; the cost comes from ignoring it. These are published maximums and reported ranges, not a prediction.
GDPR / UK GDPR, transparency and consent · EU, EEA, UK2 findings
Maximum. Up to €20 million or 4% of worldwide annual turnover, whichever is higher (Art. 83(5)); UK: up to £17.5 million or 4%.
Usually. A complaint to a data-protection authority, then a notice with a deadline to fix. Published fines against small businesses for missing notices and cookie consent have run from the low thousands of euros upward; the largest cookie-consent fines have been in the tens of millions.
Applies: Any site with users in the EU or UK, regardless of where the company is. Enforced by regulators.
GDPR / UK GDPR, security of processing · EU, EEA, UK1 finding
Maximum. Up to €10 million or 2% of worldwide annual turnover (Art. 83(4)); UK: up to £8.7 million or 2%.
Usually. Fines follow a breach, not a scan. If exposed data reaches users, breach notification to the regulator within 72 hours is mandatory and the fine considers whether the weakness was known.
Applies: Any site processing personal data of people in the EU or UK. Enforced by regulators.
CCPA / CPRA (California) · United States, California1 finding
Maximum. About $2,500 per violation and about $7,500 per intentional violation or one involving a minor, inflation-adjusted each year; each affected consumer can count as a violation.
Usually. A notice from the California Privacy Protection Agency or Attorney General; the 30-day cure period was removed in 2023. Enforcement has focused on larger companies, but the thresholds catch many startups once they pass roughly $26 million in revenue or 100,000 consumers.
Applies: Businesses over the CCPA thresholds with California users. Many early-stage sites are below them; the privacy-policy duty under CalOPPA applies to all. Enforced by regulators.
CalOPPA (California Online Privacy Protection Act) · United States, California1 finding
Maximum. Up to $2,500 per violation, enforced through California's unfair-competition law after a 30-day notice.
Usually. A notice to post a compliant policy within 30 days. Applies to any commercial site reaching Californians, with no size threshold.
Applies: Any commercial site or app collecting personal information from California residents. Enforced by regulators.
PIPEDA / Quebec Law 25 · Canada1 finding
Maximum. Quebec Law 25: administrative penalties up to CA$10 million or 2% of worldwide turnover, and penal fines up to CA$25 million or 4%. PIPEDA itself currently relies on findings and court orders.
Usually. A complaint to the Privacy Commissioner or Quebec's CAI, an investigation, and a public finding; Quebec has begun issuing monetary penalties.
Applies: Any organisation collecting personal information from people in Canada; Law 25 for Quebec residents. Enforced by regulators.
FTC Act §5 (unfair or deceptive practices) and state breach laws · United States1 finding
Maximum. No fixed fine for a first violation; the FTC obtains consent orders with 20-year audit obligations, and violating an order costs over $53,000 per day. State breach-notification laws add per-resident notification costs and, in some states, per-record penalties.
Usually. Enforcement follows an incident. An exposed live key or open database is the incident waiting to happen; the practical cost is fraud on the account plus mandatory notification.
Applies: Any US company holding consumer data. Enforced by regulators.
AI design tells
1 pattern on this page read as AI-generated: Cream / beige palette. Visitors have learned to recognize these; they read as a template and cost trust. Each one has a specific fix.
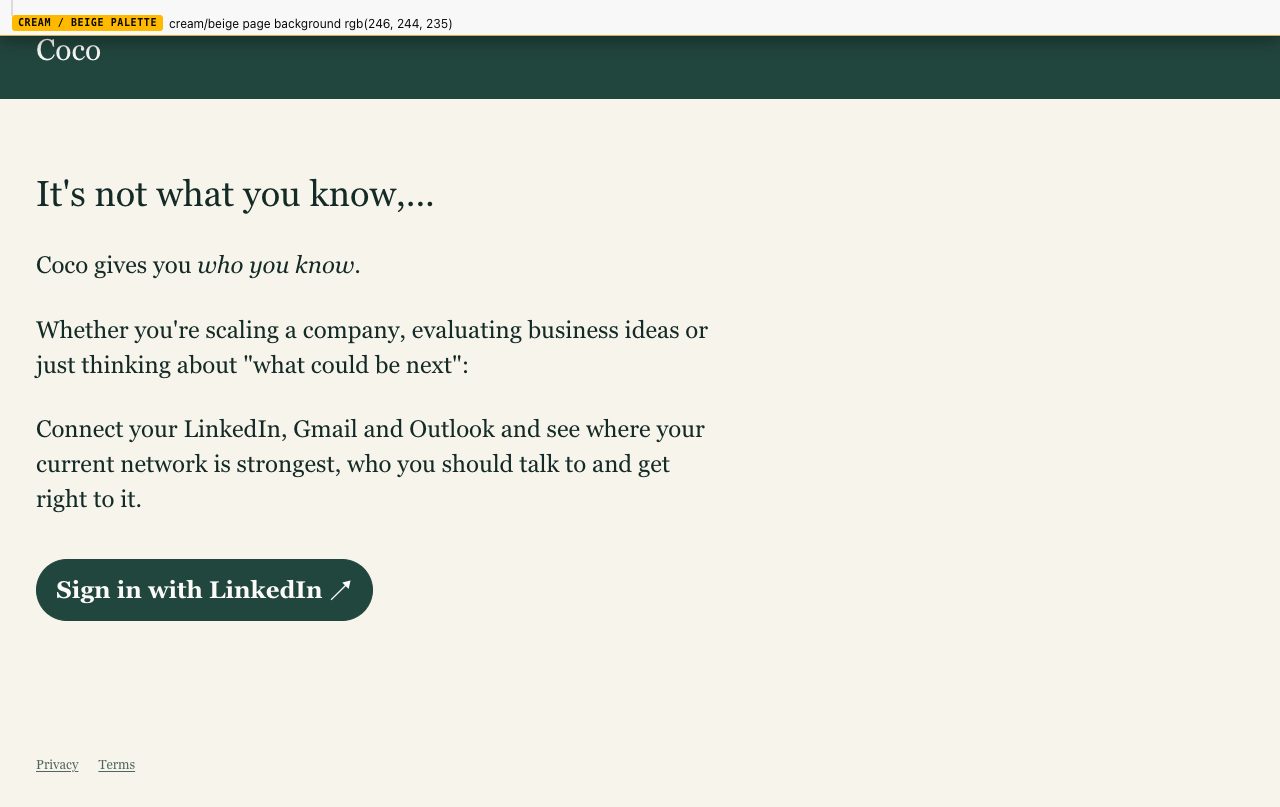
Cream / beige palette1×
A warm cream or beige page background has become the default "tasteful" AI surface, reached for by reflex. Choose a background that comes from a deliberate palette, not the safe warm off-white.
Example: cream/beige page background rgb(246, 244, 235)
Full annotated page (1 labels)
This report is complete and free, and true as of the scan time above. The next deploy, a tag added in Tag Manager or a redesigned footer can change it. Watch re-checks thisiscoco.app every day and after every deploy, emails you the moment something regresses, keeps the dated record, and gives you a trust page your customers can check.
Watch thisiscoco.appTrust page draftPassed audits
(9)
Privacy policy is present
A privacy policy link or page was found.
No third-party trackers detected
None of the common analytics or marketing pixels were found in the page.
Terms of service are present
A terms page or link was found.
Public contact or business identity present
A contact email, contact page, or mailto link was found.
No secret keys in the page or its scripts
No server-side keys (Stripe secret, OpenAI, Anthropic, AWS, GitHub, Slack, SendGrid, Supabase service_role, private keys) in the page.
1 security header set
Strict-Transport-Security
No mixed content
All referenced resources use HTTPS.
Served over HTTPS
The final URL uses TLS.
No WCAG A/AA violations found (15 rules passed)
axe-core found no violations of the WCAG 2.2 A/AA rules it can test automatically. Automated checks cover roughly a third of WCAG; manual review is still needed for the rest.
Share this report.
The link is public and shows the same free view you see here; nothing about the reader is recorded.
The certificate.
thisiscoco.app holds Clean Bill of Health WO-2026-5223, last checked November 22, 2026. Open it for the seal and what it verified.
Put your score on your README.
An embeddable badge that re-checks weekly. Builders use it the way they use a CI badge: proof the boring stuff is handled.
[](https://webopsy.tech/s/thisiscoco.app)